

Real SC-400 Exam PDF Test Engine Practice Test Questions
Microsoft SC-400 Real 2021 Braindumps Mock Exam Dumps
Microsoft SC-400 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
How to Register For Exam SC-400: Microsoft Information Protection Administrator?
NEW QUESTION 46
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You deploy the Endpoint DLP configuration package to the computers.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 47
You plan to import a file plan to the Microsoft 365 compliance center.
Which object type can you create by importing a records management file plan?
- A. retention labels
- B. retention label policies
- C. sensitivity labels
- D. sensitive info types
Answer: A
Explanation:
File plan in Records management allows you to bulk-create retention labels by importing the relevant information from a spreadsheet.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/file-plan-manager?view=o365-worldwide
NEW QUESTION 48
You plan to implement sensitivity labels for Microsoft Teams.
You need to ensure that you can view and apply sensitivity labels to new Microsoft Teams sites.
What should you do first?
- A. Configure the EnableMTPLabels Azure Active Directory (Azure AD) setting.
- B. Run the Execute-AzureAdLabelSync cmdtet.
- C. Run the Set-sposite cmdlet.
- D. Create a new sensitivity label scoped to Groups & sites.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites?view=o365-wo
NEW QUESTION 49
You have a Microsoft 365 tenant that uses the following sensitivity labels:
* Confidential
* Internal
* External
The labels are published by using a label policy named Policy1.
Users report that Microsoft Office for the wen apps do not display the Sensitivity button. The Sensitivity button appears in Microsoft 365 Apps that are installed locally.
You need to ensure that the users can apply sensitivity labels to content when they use Office for the web apps.
Solution: You run the Execute-AzureAdLabelSync cmdlet.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 50
You have a Microsoft 365 tenant that uses data loss prevention (DLP) to protect sensitive information.
You create a new custom sensitive info type that has the matching element shown in the following exhibit.
The supporting elements are configured as shown in the following exhibit.
The confidence level and character proximity are configured as shown in the following exhibit.
For each of the following statements, select Yes if statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-a-custom-sensitive-information-type?view=o365-worldwide
NEW QUESTION 51
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You deploy the Endpoint DLP configuration package to the computers.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-getting-started?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/configure-endpoints?view=o365- worldwide
NEW QUESTION 52
You enable archive mailboxes for all the users at your company.
The Default MRM Policy is shown in the MRM exhibit.
A Microsoft 365 retention label policy is shown in the Label Policy exhibit.
You need to identify the following:
* How many years until an email is archived?
* What should you modify to change the retention period for archiving?
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention?view=o365-worldwide#the-principles-of-r
NEW QUESTION 53
You have a data loss prevention (DLP) policy that applies to the Devices location. The policy protects documents that contain States passport numbers.
Users reports that they cannot upload documents to a travel management website because of the policy.
You need to ensure that the users can upload the documents to the travel management website. The solution must prevent the protected content from being uploaded to other locations.
Which Microsoft 365 Endpoint data loss prevention (Endpoint DLP) setting should you configure?
- A. File path exclusions
- B. Service domains
- C. Unallowed apps
- D. Unallowed browsers
Answer: B
Explanation:
Explanation
You can control whether sensitive files protected by your policies can be uploaded to specific service domains from Microsoft Edge.
* If the list mode is set to Block, then user will not be able to upload sensitive items to those domains.
When an upload action is blocked because an item matches a DLP policy, DLP will either generate a
* warning or block the upload of the sensitive item.
* If the list mode is set to Allow, then users will be able to upload sensitive items only to those domains, and upload access to all other domains is not allowed.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION 54
You need to meet the technical requirements for the Site3 documents.
What should you create?
- A. a retention label policy and a retention label that uses an event
- B. a sensitive info type that uses a dictionary and a sensitivity label
- C. a retention policy that has Only delete items when they reach a certain age selected
- D. a sensitive info type that uses a regular expression and a sensitivity label
Answer: A
NEW QUESTION 55
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You recently discovered that the developers at your company emailed Azure Storage keys in plain text to third parties.
You need to ensure that when Azure Storage keys are emailed, the emails are encrypted.
Solution: You configure a mail flow rule that matches the text patterns.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/exchange/policy-and-compliance/mail-flow-rules/conditions-and-exceptions?vi
NEW QUESTION 56
At the end of a project you upload project documents to a Microsoft SharePoint Online library that contains many fifes. Files that have the following naming format must be labeled as Project I
* aei_AA989.docx
* bd_WSOgadocx
* cei_DLF112-docx
* ebc_QQ4S4.docx
* ecc_BB565.docx
You plan to create an auto-apply retention label policy.
What should you use to identify the files, and which regular expression should you use? To answer, select the appropriate options in the answer area.
Answer:
Explanation: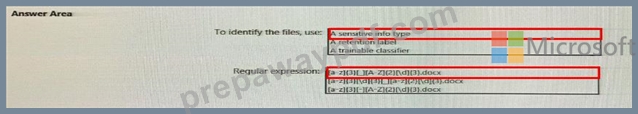
NEW QUESTION 57
You create a retention label that has a retention period of seven years.
You need to ensure that documents containing a credit card number are retained for seven years. Other documents must not be retained.
What should you create?
- A. a retention policy that deletes files automatically
- B. a retention policy that retains files automatically
- C. a retention label policy of type auto-apply
- D. a retention label policy of type publish
Answer: D
NEW QUESTION 58
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant and 500 computers that run Windows 10. The computers are onboarded to the Microsoft 365 compliance center.
You discover that a third-party application named Tailspin_scanner.exe accessed protected sensitive information on multiple computers. Tailspin_scanner.exe is installed locally on the computers.
You need to block Tailspin_scanner.exe from accessing sensitive documents without preventing the application from accessing other documents.
Solution: From the Cloud App Security portal, you create an app discovery policy.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
You can create app discovery policies to alert you when new apps are detected within your organization.
Use the unallowed apps list instead.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/cloud-discovery-policies
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION 59
You need to automatically apply a sensitivity label to documents that contain information about your company's network including computer names, IP addresses, and configuration information.
Which two objects should you use? Each correct answer presents part of the solution. (Choose two.) NOTE: Each correct selection is worth one point.
- A. an Information protection auto-labeling policy
- B. a sensitivity label that has auto-labeling
- C. a sensitive info type that uses a regular expression
- D. a sensitive info type that uses keywords
- E. a data loss prevention (DLP) policy
- F. a custom trainable classifier
Answer: A,F
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/classifier-learn-about?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365- worldwide
NEW QUESTION 60
You have a Microsoft SharePoint Online site that contains employee contracts in a document library named Contracts.
The contracts must be treated as records in accordance with your company's records management policy.
You need to implement a solution to automatically mark all the contracts as records when they are uploaded to Contracts.
Which two actions should you perform? Each correct answer presents part of the solution. (Choose two.) NOTE: Each correct selection is worth one point.
- A. Create a sensitivity label.
- B. Create a retention policy.
- C. Create a retention label.
- D. Configure a default label on the Contracts document library.
- E. Create a SharePoint Records Center.
- F. Create a retention lock.
Answer: C,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-apply-retention-labels?view=o365-worldwide
NEW QUESTION 61
You have a data loss prevention (DLP) policy that has the advanced DLP rules shown in the following table.
You need to identify which rules will apply when content matches multiple advanced DLP rules.
Which rules should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwide
NEW QUESTION 62
You need to implement a solution to encrypt email. The solution must meet the compliance requirements.
What should you create in the Exchange admin center and the Microsoft 36.S compliance center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 63
You use project codes that have a format of three alphabetical characters that represent the project type, followed by three digits, for example Abc123.
You need to create a new sensitive info type for the project codes.
How should you configure the regular expression to detect the content? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://joannecklein.com/2018/08/07/build-and-use-custom-sensitive-information-types-in-office-365/
Topic 1, Fabrikam, Case Study
Overview
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each there may be additional case studies and sections on this exam. You must manage you're your time to ensure that you are able to complete all included on this exam in the time provided.
To answer the questions included in a case study, you will need In reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described In the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab. note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Cloud Environment
Fabrikam has a Microsoft 365 tenant that contains the following resources:
* An Azure Active Directory (Azure AD) tenant that syncs to an on-premises Active Directory domain named corp.fabrikam.com
* Microsoft Cloud App Security connectors configured for all supported cloud applications used by the company Some users have company Dropbox accounts.
Compliance Configuration
Fabrikam has the following in the Microsoft 365 compliance center:
* A data loss prevention (DLP) policy is configured. The policy displays a tooltip to users. Users can provide a business justification to override a DLP policy violation.
* The Azure information Protection unified labeling scanner is installed and configured.
* A sensitivity label named Fabrikam Confidential is configured.
An existing third-party records management system is managed by the compliance department.
Human Resources (HR) Management System
The HR department has an Azure SQL. database that contains employee information. Each employee has a unique 12-character alphanumeric ID. The database contains confidential employed attributes including payroll information, date of birth, and personal contact details.
On-premises Environment
You have an on premises file server that runs Windows Server 2019 and stores Microsoft Office documents in a shared folder named Data.
All end-user computers are joined to the corp.fabrinkam.com domain and run a third-party antimalware application.
Sales Contracts
Users in the sales department receive draft sales contracts from customers by email. The sales contracts are written by the customers and are not in a standard format.
Employment Applications
Employment applications and resumes are received by HR department managers and stored in either mailboxes, Microsoft SharePoint Online sites, OneDrive for Business folders, or Microsoft Teams channels.
The employment application form is downloaded from SharePoint Online and a serial number is assigned to each application.
the resumes are written by the applications and in any format.
HR Requirements
You need to create a DLP policy that will notify the HR department of a DLP policy violation if a document that contains confidential employee attributes is shared externally. The DLP policy must use an Exact Data Match (EDM) classification derived from a CSV export of the HR department database.
The HR department identifies the following requirements for handling employment applications:
* Resumes must be identified automatically based on similarities to other resumes received in the past
* Employment applications and resumes must be deleted automatically two years after the applications are received.
* Documents and emails that contain an application serial number must be identified automatically and marked as an employment application.
Sales Requirements
A sensitivity label named Sales Contract must be applied automatically to all draft and finalized sales contracts.
Compliance Requirements
Fabrikam identifies the following compliance requirements:
* All DLP policies must be applied to computers that run Windows 10, with the least possible changes to the computers.
* Users in the compliance department must view the justification provided when a user receives a tooltip notification for a DLP violation.
* If a document that has the Fabrikam Confidential sensitivity label applied is uploaded to Dropbox. the file must be deleted automatically. - The Fabrikam Confidential sensitivity label must be applied to existing Microsoft Word documents in the Data shared folder that have a document footer containing the following string: Company use only.
* Users must be able to manually select that email messages are sent encrypted. The encryption will use Office
365 Message Encryption (OME) v2. Any email containing an attachment that has the Fabrikam Confidential sensitivity label applied must be encrypted automatically by using OME.
* Existing policies configured in the third-party records management system must be replaced by using Records management in the Microsoft 365 compliance center. The compliance department plans to export the existing policies, and then produce a CSV file that contains matching labels and policies that are compatible with records management in Microsoft 365. The CSV file must be used to configure records management in Microsoft 365.
Executive Requirements
You must be able to restore all email received by Fabrikam executives for up to three years after an email is received, even if the email was deleted permanently.
NEW QUESTION 64
......
Exam SC-400: Microsoft Information Protection Administrator
The Information Protection Administrator plans and implements controls that meet organizational compliance needs. This person is responsible for translating requirements and compliance controls into technical implementation. They assist organizational control owners to become and stay compliant.
They work with information technology (IT) personnel, business application owners, human resources, and legal stakeholders to implement technology that supports policies and controls necessary to sufficiently address regulatory requirements for their organization. They also work with the compliance and security leadership such as a Chief Compliance Officer and Security Officer to evaluate the full breadth of associated enterprise risk and partner to develop those policies.
This person defines applicable requirements and tests IT processes and operations against those policies and controls. They are responsible for creating policies and rules for content classification, data loss prevention, governance, and protection.
Part of the requirements for: Microsoft Certified: Information Protection Administrator Associate
Prepare For The SC-400 Question Papers In Advance: https://www.prepawaypdf.com/Microsoft/SC-400-practice-exam-dumps.html
Released Microsoft SC-400 Updated Questions PDF: https://drive.google.com/open?id=1Y1kPILl_qU-ZoLkCe48TPwJFjbdNKX0_