

[Jan 12, 2022] Fully Updated Dumps PDF - Latest SC-400 Exam Questions and Answers
100% Free SC-400 Exam Dumps to Pass Exam Easily from PrepAwayPDF
Microsoft SC-400 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
NEW QUESTION 70
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant and 500 computers that run Windows 10. The computers are onboarded to the Microsoft 365 compliance center.
You discover that a third-party application named Tailspin_scanner.exe accessed protected sensitive information on multiple computers. Tailspin_scanner.exe is installed locally on the computers.
You need to block Tailspin_scanner.exe from accessing sensitive documents without preventing the application from accessing other documents.
Solution: From the Cloud App Security portal, you mark the application as Unsanctioned.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION 71
You have a Microsoft 365 tenant.
You create the following:
* A sensitivity label
* An auto-labeling policy
You need to ensure that the sensitivity label is applied to all the data discovered by the auto-labeling policy.
What should you do first?
- A. Create a trainable classifier.
- B. Enable insider risk management.
- C. Run the Enable-TransportRule cmdlet.
- D. Run the policy in simulation mode.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-wo
NEW QUESTION 72
You have a data loss prevention (DLP) policy that applies to the Devices location. The policy protects documents that contain States passport numbers.
Users reports that they cannot upload documents to a travel management website because of the policy.
You need to ensure that the users can upload the documents to the travel management website. The solution must prevent the protected content from being uploaded to other locations.
Which Microsoft 365 Endpoint data loss prevention (Endpoint DLP) setting should you configure?
- A. Service domains
- B. Unallowed browsers
- C. File path exclusions
- D. Unallowed apps
Answer: A
Explanation:
Explanation
You can control whether sensitive files protected by your policies can be uploaded to specific service domains from Microsoft Edge.
* If the list mode is set to Block, then user will not be able to upload sensitive items to those domains.
When an upload action is blocked because an item matches a DLP policy, DLP will either generate a
* warning or block the upload of the sensitive item.
* If the list mode is set to Allow, then users will be able to upload sensitive items only to those domains, and upload access to all other domains is not allowed.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION 73
You have a Microsoft 365 tenant.
All Microsoft OneDrive for Business content is retained roe five years.
A user named User1 left your company a year ago, after which the account of User 1 was deleted from Azure Active Directory (Azure AD) You need to recover an important file that was stored in the OneDrive of User1.
What should you use?
- A. Deleted users in the Microsoft 365 admin center
- B. the OneDrive recycle bin
- C. the Restore-SPODeletedSite PowerShell cmdlet
- D. the Restore-ADObject PowerShell cmdlet
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/onedrive/set-retention
https://docs.microsoft.com/en-us/onedrive/retention-and-deletion
NEW QUESTION 74
You plan to implement sensitivity labels for Microsoft Teams.
You need to ensure that you can view and apply sensitivity labels to new Microsoft Teams sites.
What should you do first?
- A. Create a new sensitivity label scoped to Groups & sites.
- B. Configure the EnableMTPLabels Azure Active Directory (Azure AD) setting.
- C. Run the Set-sposite cmdlet.
- D. Run the Execute-AzureAdLabelSync cmdtet.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites?view=o365-worldwide
NEW QUESTION 75
How many files in Site2 will be visible to User1 and User2 after you turn on DLPpolicy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.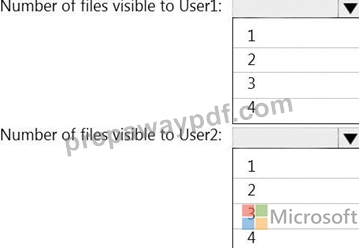
Answer:
Explanation: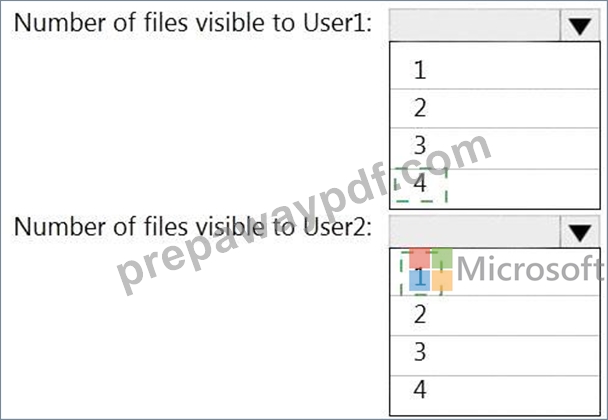
Explanation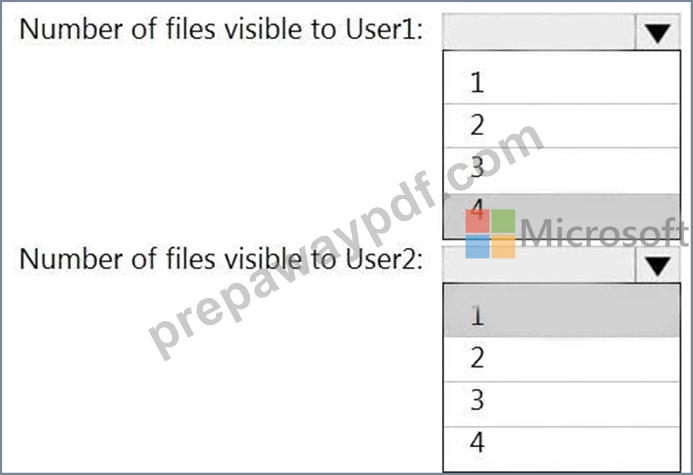
Reference:
https://social.technet.microsoft.com/wiki/contents/articles/36527.implement-data-loss-prevention-dlp-in-sharepo
NEW QUESTION 76
You have a Microsoft 365 tenant that uses Microsoft Teams.
You create a data loss prevention (DLP) policy to prevent Microsoft Teams users from sharing sensitive information.
You need to identify which locations must be selected to meet the following requirements:
Documents that contain sensitive information must not be shared inappropriately in Microsoft Teams.
If a user attempts to share sensitive information during a Microsoft Teams chat session, the message must be deleted immediately.
Which three locations should you select? To answer, select the appropriate locations in the answer are a. (Choose three.) NOTE: Each correct selection is worth one point.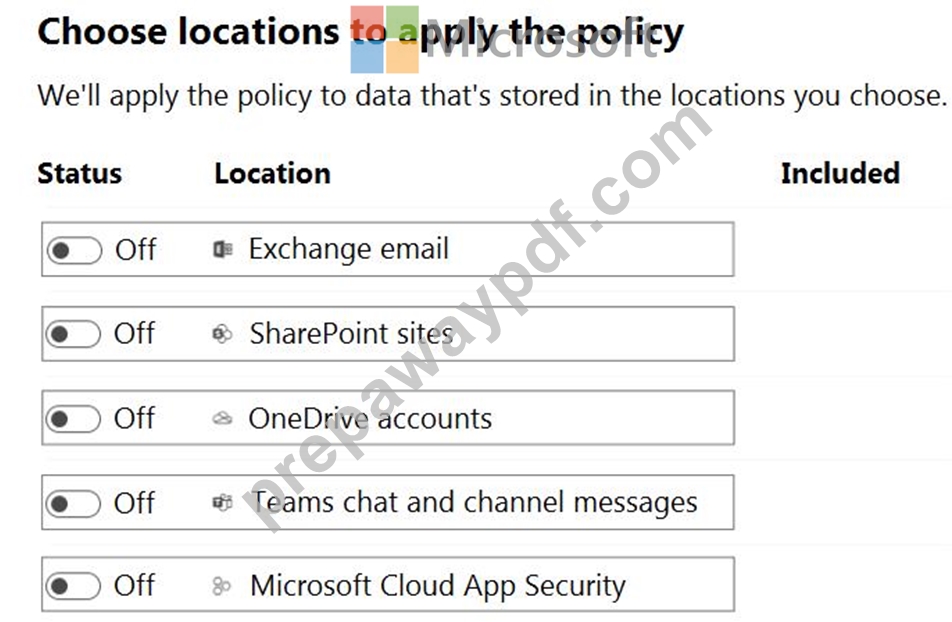
Answer:
Explanation: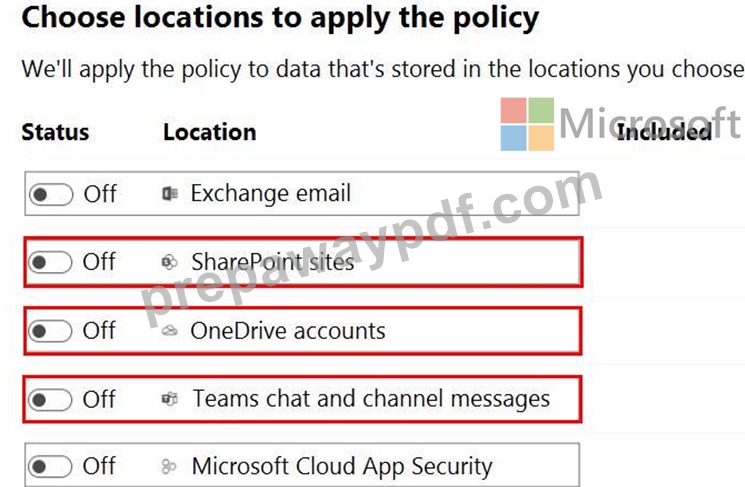
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-microsoft-teams?view=o365-worldwide
NEW QUESTION 77
You need to meet the technical requirements for the creation of the sensitivity labels. Which administrative users are currently missing the Sensitivity label administrator role?
- A. Admin1 only
- B. Admm1, Admin2, Admin4, and Admin5 only
- C. Admin 1 and Admin5 only
- D. Admin 1. Admin2, and Admin3 only
- E. Admin 1 and Admin4 only
Answer: D
NEW QUESTION 78
You need to recommend a solution that meets the Data Loss Prevention requirements for the HR department.
Which three actions should you perform? Each correct answer presents part of the solution. (Choose three.) NOTE: Each correct selection is worth one point.
- A. Schedule EdmUploadAgent.exe to hash and upload a data file that contains employee information.
- B. Create a sensitive info type rule package that contains the EDM classification.
- C. Create a sensitive info type rule package that contains regular expressions.
- D. Define the sensitive information database schema in the XML format.
- E. Define the sensitive information database schema in the CSV format.
Answer: A,B,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-custom-sensitive-information-types-withexact-data-match-based-classification?view=o365-worldwide
NEW QUESTION 79
You need to test Microsoft Office 365 Message Encryption (OME) capabilities for your company. The test must verify the following information:
The acquired default template names
The encryption and decryption verification status
Which PowerShell cmdlet should you run?
- A. Test-Mailflow
- B. Test-OAuthConnectivity
- C. Test-IRMConfiguration
- D. Test-ClientAccessRule
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/set-up-new-message-encryption-capabilities?
view=o365-worldwide
NEW QUESTION 80
You plan to create a custom trainable classifier based on an organizational form template.
You need to identity which role based access control (RBAC ) role is required to create the trainable classifier and where to classifier. The solution must use the principle of least privilege.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.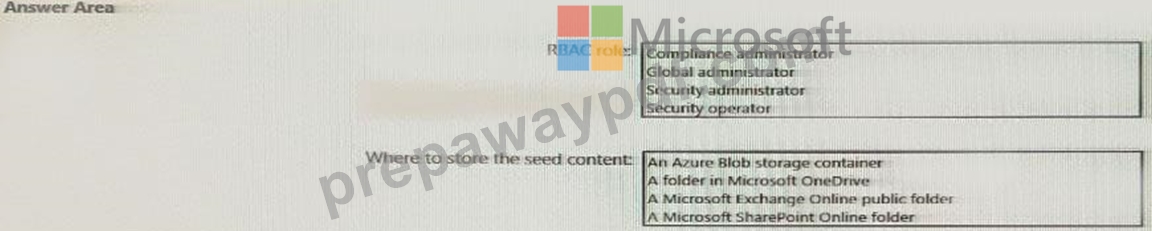
Answer:
Explanation:
Text Description automatically generated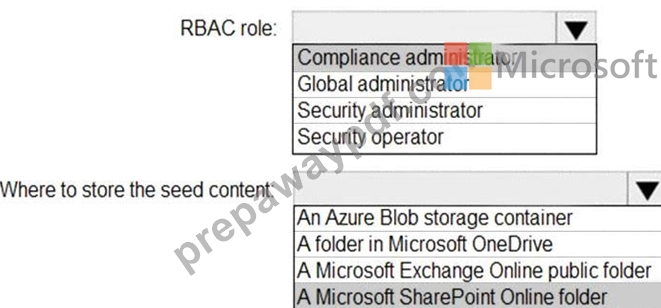
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/classifier-get-started-with?view=o365-worldwide#p
NEW QUESTION 81
While creating a retention label, you discover that the following options are missing:
* Mark items as a record
* Mark items are a regular record
You need to ensure that the options are available when you create label in the Microsoft 365 compliance center.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.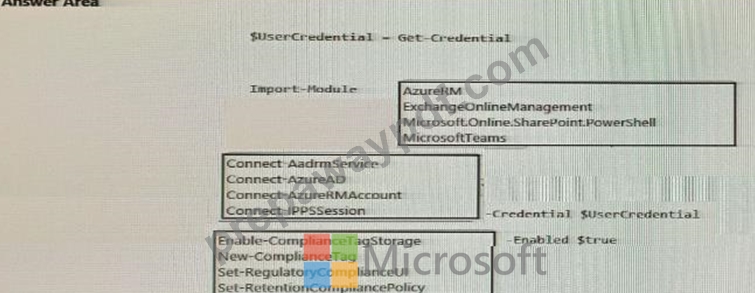
Answer:
Explanation: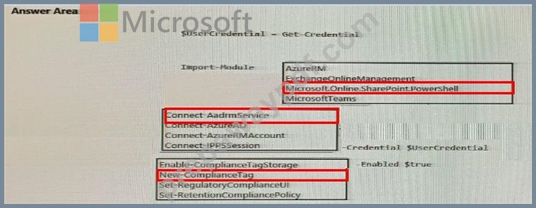
NEW QUESTION 82
You need to be alerted when users share sensitive documents from Microsoft OneDrive to any users outside your company.
What should you do?
- A. From the Microsoft 36h compliance? center, create an insider risk policy.
- B. From the Microsoft 365 compliance center, start a data investigation.
- C. From the Azure portal, create an Azure Active Directory (Azure Al)) Identity Protection policy.
- D. From the Microsoft 365 compliance center, create a data loss prevention (DLP) policy.
Answer: C
NEW QUESTION 83
You need to recommend a solution that meets the executive requirements. What should you recommend?
- A. From the Microsoft 365 compliance center, create a retention label.
- B. From the Microsoft 365 compliance center, create a retention policy.
- C. From the Microsoft 365 compliance center, create a DLP policy.
- D. From the Exchange admin center, enable archive mailboxes.
Answer: C
NEW QUESTION 84
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender for Endpoint.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-getting-started?view=o365-worldwide
NEW QUESTION 85
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth is worth one point.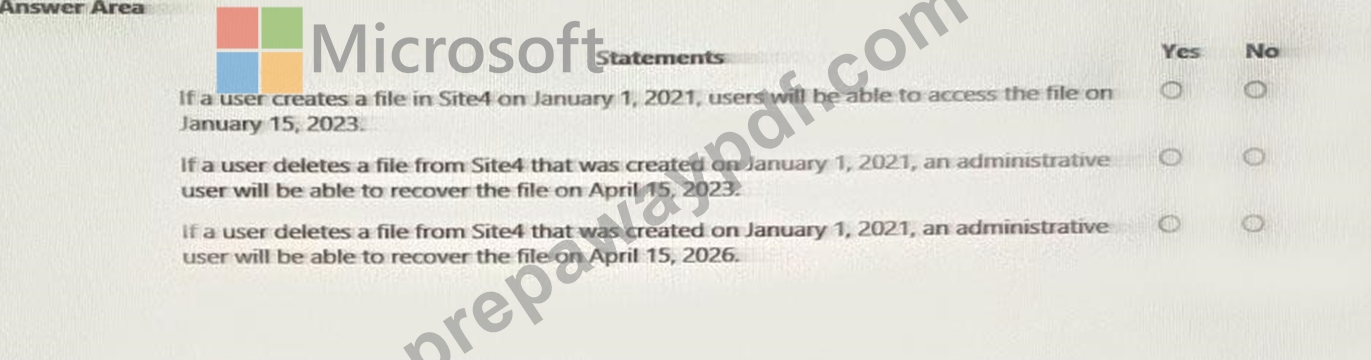
Answer:
Explanation: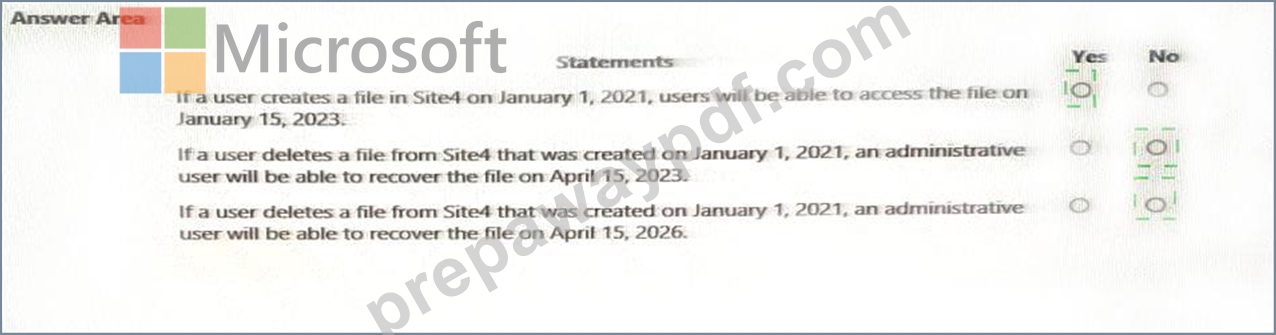
NEW QUESTION 86
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant and 500 computers that run Windows 10. The computers are onboarded to the Microsoft 365 compliance center.
You discover that a third-party application named Tailspin_scanner.exe accessed protected sensitive information on multiple computers. Tailspin_scanner.exe is installed locally on the computers.
You need to block Tailspin_scanner.exe from accessing sensitive documents without preventing the application from accessing other documents.
Solution: From the Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings, you add the application to the unallowed apps list.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Explanation
Unallowed apps is a list of applications that you create which will not be allowed to access a DLP protected file.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION 87
You have a Microsoft 365 tenant that uses data loss prevention (DLP).
You have a custom employee information form named Template 1.docx.
You need to create a classification rule package based on the document fingerprint of Templatel.docx.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.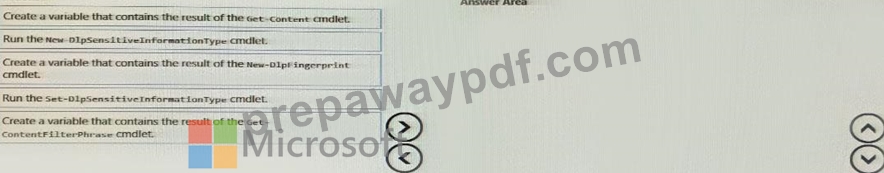
Answer:
Explanation: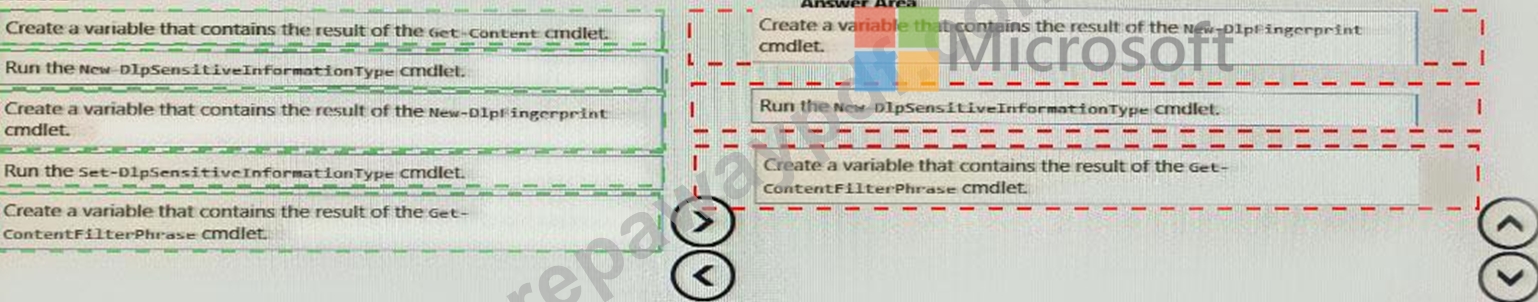
NEW QUESTION 88
At the end of a project, you upload project documents to a Microsoft SharePoint Online library that contains many files. The following is a sample of the project document file names:
* aei_AA989.docx
* bci_WS098.docx
* cei_DF112.docx
* ebc_QQ454.docx
* ecc_BB565.docx
All documents that use this naming format must be labeled as Project Documents:
You need to create an auto-apply retention label policy.
What should you use to identify the files?
- A. A sensitive info type
- B. A retention label
- C. A trainable classifier
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/classifier-get-started-with?view=o365-worldwide
NEW QUESTION 89
You plan to create a custom trainable classifier based on an organizational form template.
You need to identity which role based access control (RBAC ) role is required to create the trainable classifier and where to classifier. The solution must use the principle of least privilege.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.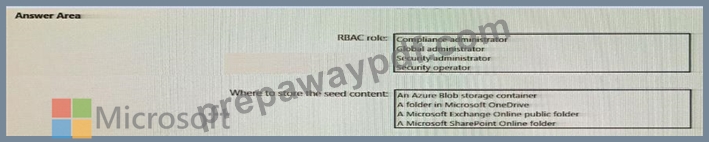
Answer:
Explanation: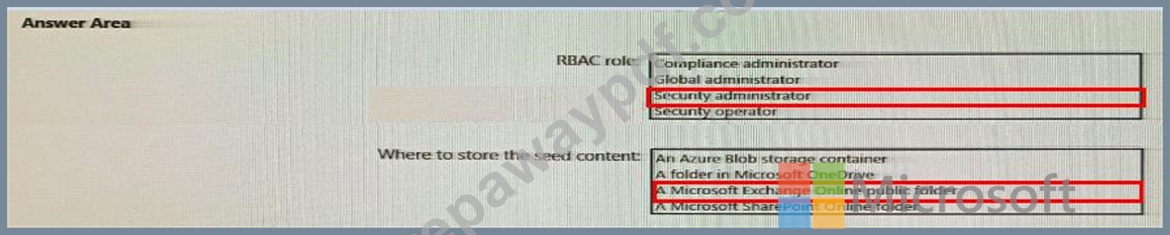
NEW QUESTION 90
You create a retention label policy named Contoso_policy that contains the following labels.
10 years then delete
5 years then delete
Do not retain
Contoso_Policy is applied to content In Microsoft Sharepoint Online sites.
After a couple of days, yon discover the following messages on the Properties page of the label policy.
* Statue Off (Error)
* It's taking longer than expected to deploy the policy
You need to reinitiate the policy.
How should you complete the command? To answer, select the appropriate options in the; answer area.
NOTE: Each correct selection is worth one point.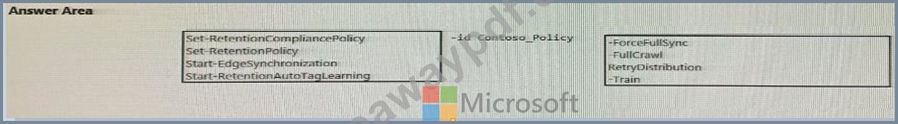
Answer:
Explanation: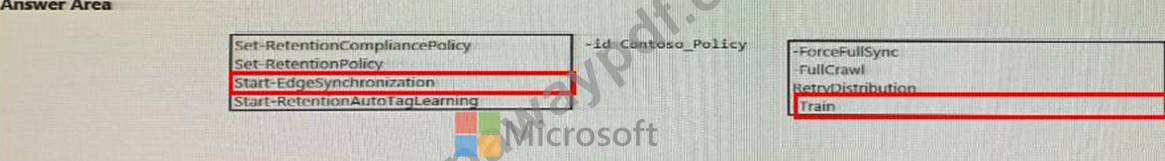
NEW QUESTION 91
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You deploy the Endpoint DLP configuration package to the computers.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION 92
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring a file policy in Microsoft Cloud App Security.
You need to configure the policy to apply to all files. Alerts must be sent to every file owner who is affected by the policy. The policy must scan for credit card numbers, and alerts must be sent to the Microsoft Teams site of the affected department.
Solution: You use the Data Classification service inspection method and send alerts as email.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/dcs-inspection
https://docs.microsoft.com/en-us/cloud-app-security/data-protection-policies
NEW QUESTION 93
......
Free SC-400 Exam Questions SC-400 Actual Free Exam Questions: https://www.prepawaypdf.com/Microsoft/SC-400-practice-exam-dumps.html
Verified SC-400 dumps and 125 unique questions: https://drive.google.com/open?id=1ts2BaAZwlx3muaW64n_F37HtqmOQgmM2