

Latest SC-400 Pass Guaranteed Exam Dumps with Accurate & Updated Questions
SC-400 Exam Brain Dumps - Study Notes and Theory
Exam SC-400: Microsoft Information Protection Administrator
The Information Protection Administrator plans and implements controls that meet organizational compliance needs. This person is responsible for translating requirements and compliance controls into technical implementation. They assist organizational control owners to become and stay compliant.
They work with information technology (IT) personnel, business application owners, human resources, and legal stakeholders to implement technology that supports policies and controls necessary to sufficiently address regulatory requirements for their organization. They also work with the compliance and security leadership such as a Chief Compliance Officer and Security Officer to evaluate the full breadth of associated enterprise risk and partner to develop those policies.
This person defines applicable requirements and tests IT processes and operations against those policies and controls. They are responsible for creating policies and rules for content classification, data loss prevention, governance, and protection.
Part of the requirements for: Microsoft Certified: Information Protection Administrator Associate
NEW QUESTION 56
You need to meet the technical requirements for the confidential documents.
What should you created first, and what should you use for the detection method? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.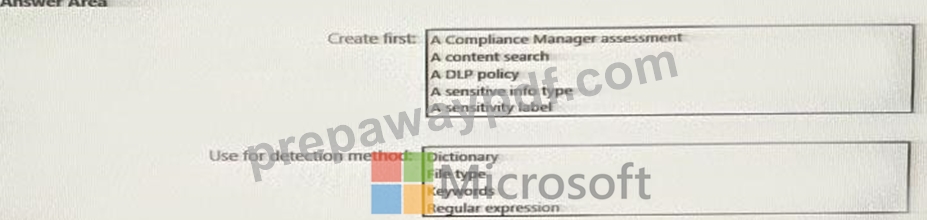
Answer:
Explanation: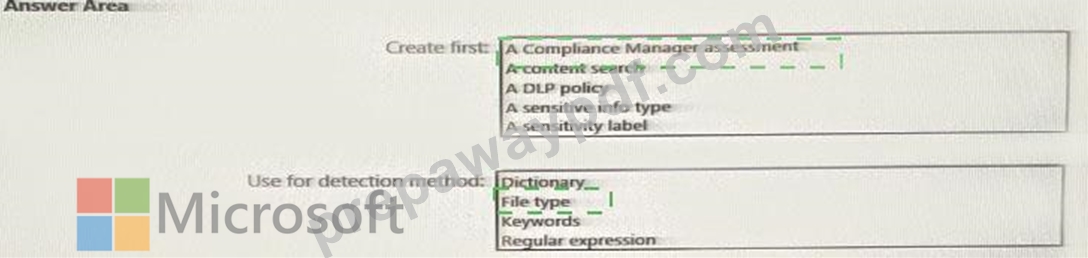
NEW QUESTION 57
While creating a retention label, you discover that the following options are missing:
* Mark items as a record
* Mark items are a regular record
You need to ensure that the options are available when you create label in the Microsoft 365 compliance center.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.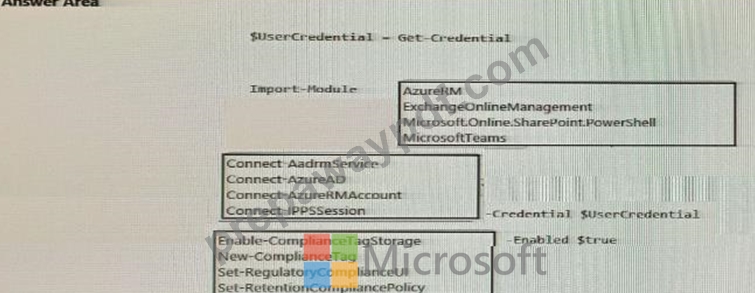
Answer:
Explanation: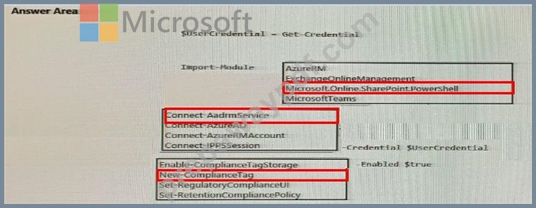
NEW QUESTION 58
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring a file policy in Microsoft Cloud App Security.
You need to configure the policy to apply to all files. Alerts must be sent to every file owner who is affected by the policy. The policy must scan for credit card numbers, and alerts must be sent to the Microsoft Teams site of the affected department.
Solution: You use the Built-in DLP inspection method and send alerts as email.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
Alerts must be sent to the Microsoft Teams site of the affected department. A Microsoft Power Automate playbook should be used.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/content-inspection-built-in
https://docs.microsoft.com/en-us/cloud-app-security/flow-integration
NEW QUESTION 59
Your company has a Microsoft 365 tenant that uses a domain named contoso.com.
You are implementing data loss prevention (DLP).
The company's default browser is Microsoft Edge.
During a recent audit, you discover that some users use Firefox and Google Chrome browsers to upload files labeled as Confidential to a third-party Microsoft SharePoint Online site that has a URL of https://m365x076709.sharepoint.com. Users are blocked from uploading the confidential files to the site from Microsoft Edge.
You need to ensure that the users cannot upload files labeled as Confidential from Firefox and Google Chrome to any cloud services.
Which two actions should you perform? Each correct answer presents part of the solution. (Choose two.) NOTE: Each correct selection is worth one point.
- A. Create a DLP policy that applies to the Devices location.
- B. From the Microsoft 365 Endpoint data loss prevention (Endpoint) DLP settings, add m365x076709.sharepoint.com as a blocked service domain.
- C. From the Microsoft 365 compliance center, onboard the devices.
- D. From the Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings, add Firefox and Google Chrome to the unallowed browsers list.
- E. From the Microsoft 365 Endpoint data loss prevention (Endpoint) DLP settings, add contoso.com as an allowed service domain.
Answer: C,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-learn-about?view=o365-worldwide
NEW QUESTION 60
You plan to implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You need to identify which end user activities can be audited on the endpoints, and which activities can be restricted on the endpoints.
What should you identify for each activity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.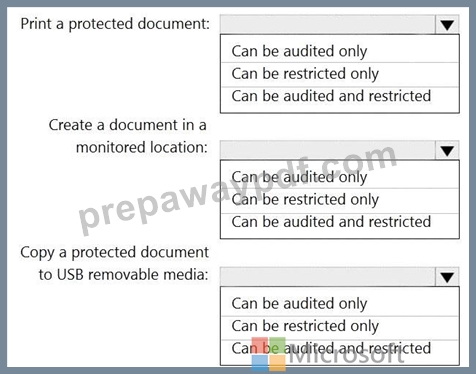
Answer:
Explanation: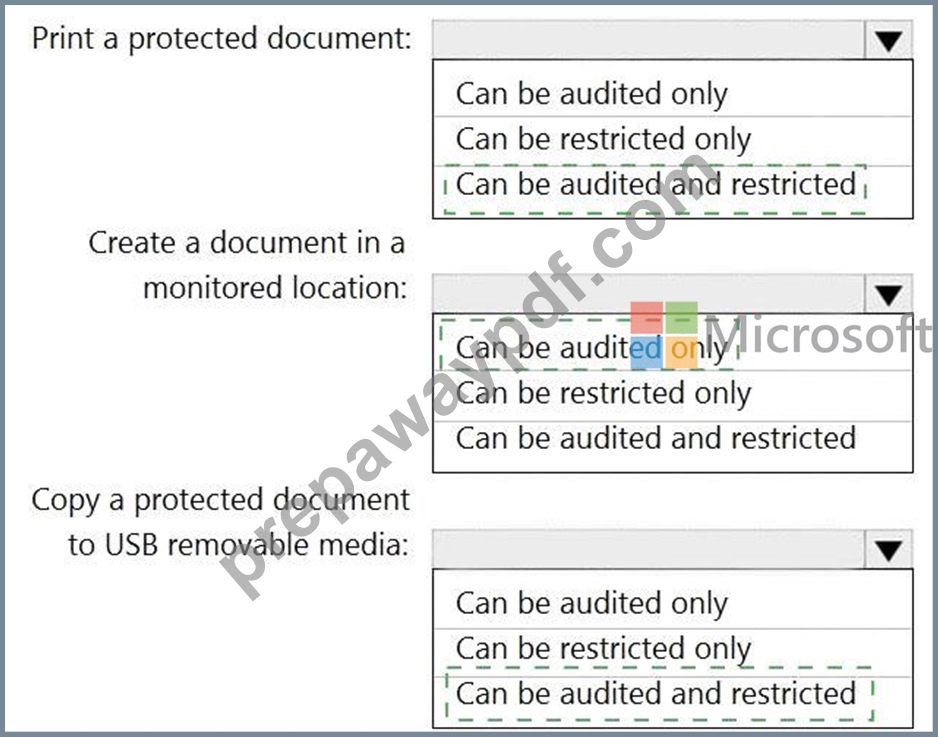
Explanation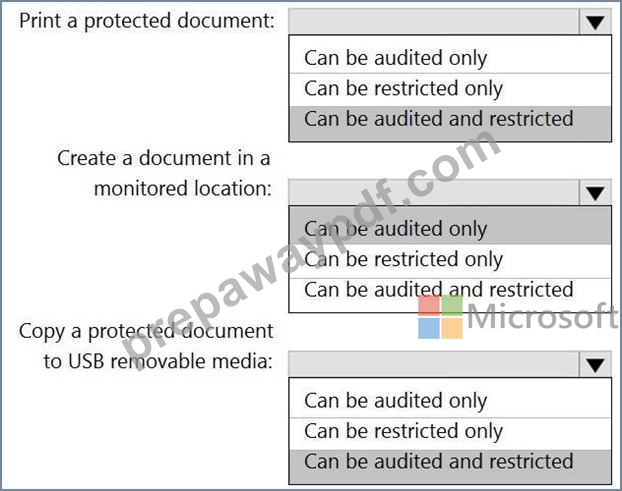
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-learn-about?view=o365-worldwide
NEW QUESTION 61
You need to protect documents that contain credit card numbers from being opened by users outside your company. The solution must ensure that users at your company can open the documents.
What should you use?
- A. a sensitivity label policy
- B. a retention policy
- C. a data loss prevention (DLP) policy
- D. a sensitivity label
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-learn-about-dlp?view=o365-worldwide
NEW QUESTION 62
You need to implement a solution to encrypt email. The solution must meet the compliance requirements.
What should you create in the Exchange admin center and the Microsoft 36.S compliance center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.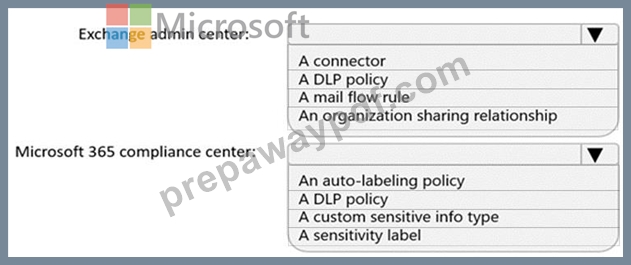
Answer:
Explanation: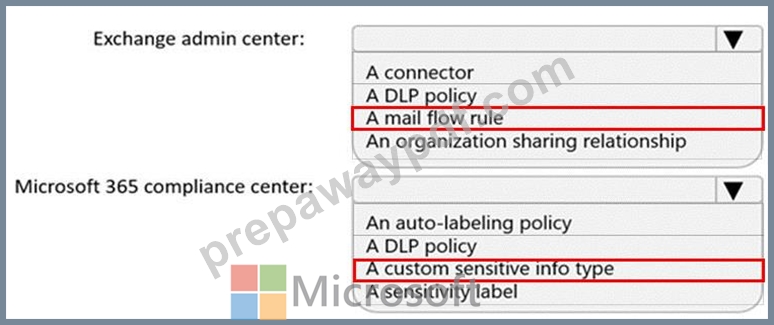
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome-sensitive-info-types?view=o365-worldwide
NEW QUESTION 63
You have a Microsoft 365 tenant that uses the following sensitivity labels:
* Confidential
* Internal
* External
The labels are published by using a label policy named Policy1.
Users report that Microsoft Office for the wen apps do not display the Sensitivity button. The Sensitivity button appears in Microsoft 365 Apps that are installed locally.
You need to ensure that the users can apply sensitivity labels to content when they use Office for the web apps.
Solution: You modify the publishing settings of Policy1.
Does the meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 64
You need to recommend a solution that meets the compliance requirements for viewing DLP tooltip justifications.
What should you recommend?
- A. Configure an Azure logic app to route DLP notification emails to the compliance department.
- B. Configure a Microsoft Power Automate workflow to route DLP notification emails to the compliance department.
- C. Instruct the compliance department users to review the False positive and override report.
- D. Instruct the compliance department users to review the DLP incidents report.
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/view-the-dlp-reports?view=o365-worldwide
NEW QUESTION 65
You create a retention label policy named Contoso_policy that contains the following labels.
* 10 years then delete
* 5 years then delete
* Do not retain
Contoso_Policy is applied to content In Microsoft Sharepoint Online sites.
After a couple of days, yon discover the following messages on the Properties page of the label policy.
* Statue Off (Error)
* It's taking longer than expected to deploy the policy
You need to reinitiate the policy.
How should you complete the command? To answer, select the appropriate options in the; answer area.
NOTE: Each correct selection is worth one point.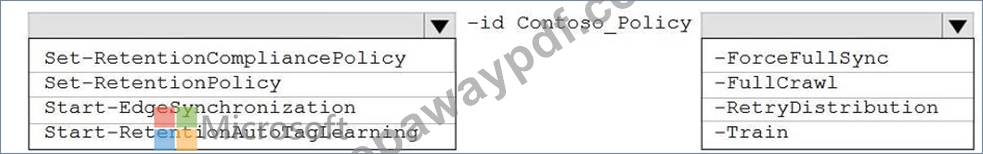
Answer:
Explanation:
Explanation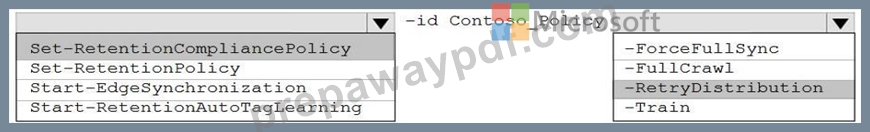
Reference:
https://docs.microsoft.com/en-us/powershell/module/exchange/set-retentioncompliancepolicy?view=exchange-p
NEW QUESTION 66
You have a Microsoft 365 tenant that uses records management.
You use a retention label to mark legal files stored in a Microsoft SharePoint Online document library as regulatory records.
What can you do to the legal files?
- A. Remove the retention label of the files.
- B. Move the files to a different folder within the document library.
- C. Edit the properties of the files.
- D. Delete the content from the files.
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/records-management?view=o365- worldwide#records
NEW QUESTION 67
While creating a retention label, you discover that the following options are missing:
* Mark items as a record
* Mark items are a regular record
You need to ensure that the options are available when you create label in the Microsoft 365 compliance center.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.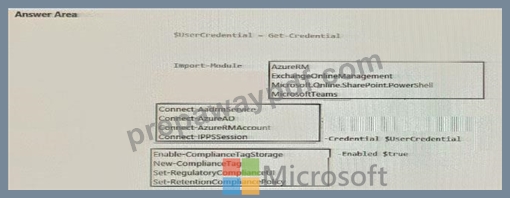
Answer:
Explanation: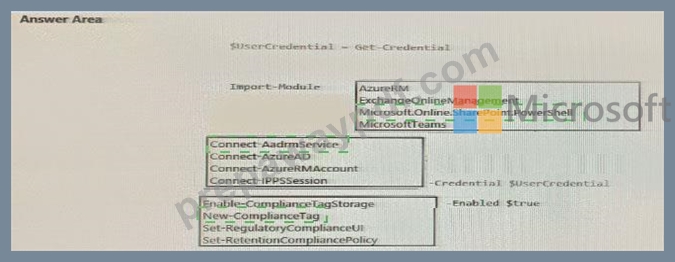
NEW QUESTION 68
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You enroll the computers in Microsoft intune.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-getting-started?view=o365-worldwide
NEW QUESTION 69
While creating a retention label, you discover that the following options are missing:
* Mark items as a record
* Mark items are a regular record
You need to ensure that the options are available when you create label in the Microsoft 365 compliance center.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.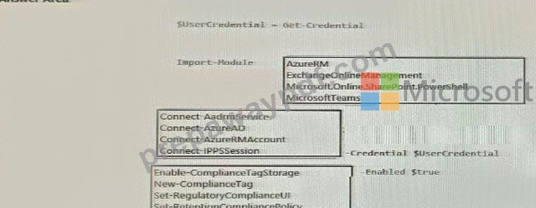
Answer:
Explanation: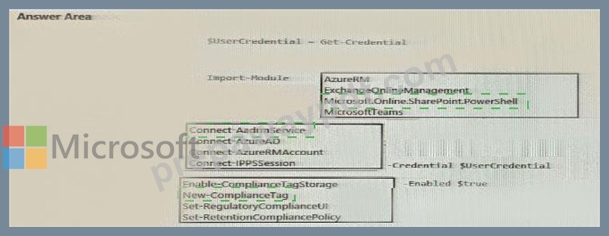
NEW QUESTION 70
You create a retention label that has a retention period of seven years.
You need to ensure that documents containing a credit card number are retained for seven years. Other documents must not be retained.
What should you create?
- A. a retention policy that deletes files automatically
- B. a retention policy that retains files automatically
- C. a retention label policy of type auto-apply
- D. a retention label policy of type publish
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-retention-labels-automatically?view=o365-wo
NEW QUESTION 71
Each product group at your company must show a distinct product logo in encrypted emails instead of the standard Microsoft Office 365 logo.
What should you do to create the branding templates?
- A. Create an RMS template.
- B. Create a Transport rule.
- C. Run the Set-IRMConfiguration cmdlet.
- D. Run the New-OMEConfiguration cmdlet.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/add-your-organization-brand-to-encryptedmessages?
NEW QUESTION 72
You create three sensitivity labels named Sensitivity1, Sensitivity2, and Sensitivity3 and perform the following actions:
Publish Sensitivity1.
Create an auto-labeling policy for Sensitivity2.
You plan to create a file policy named Policy1 in Microsoft Cloud App Security.
Which sensitivity labels can you apply to Microsoft SharePoint Online in Policy1?
- A. Sensitivity1, Sensitivity2, and Sensitivity3
- B. Sensitivity1 only
- C. Sensitivity1 and Sensitivity2 only
- D. Sensitivity2 only
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365- worldwide
https://docs.microsoft.com/en-us/cloud-app-security/azip-integration
NEW QUESTION 73
You have a Microsoft SharePoint Online site named Site1 and a sensitivity label named Sensitivity1. Sensitivity1 adds a watermark and a header to content.
You create a policy to automatically apply Sensitivity1 to emails in Microsoft Exchange Online and Site1.
How will Sensitivity1 mark matching emails and Site1 documents? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.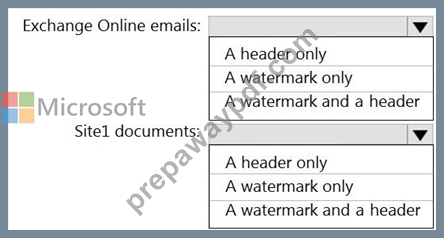
Answer:
Explanation: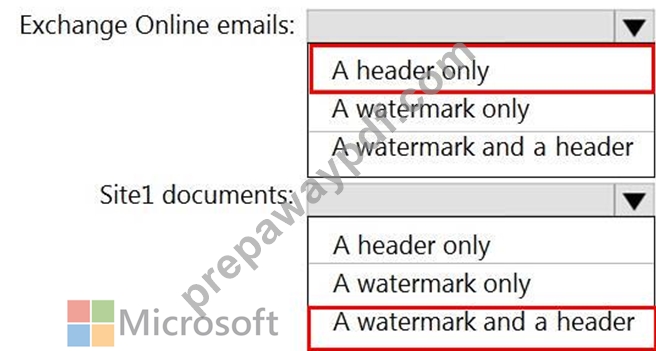
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION 74
You have a data loss prevention (DLP) policy configured for endpoints as shown in the following exhibit.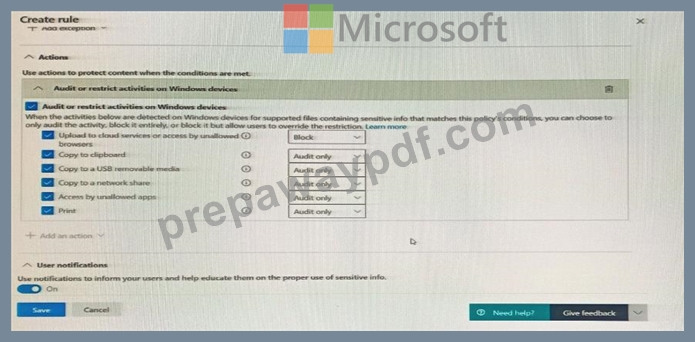
From a computer named Computer1, 3 user can sometimes upload files to cloud services and sometimes cannot. Other users experience the same issue. What are two possible causes of the issue? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
- A. The Copy to clipboard action is set to Audit only.
- B. The computers are NOT onboarded to the Microsoft 365 compliance center.
- C. There are file path exclusions in the Microsoft 365 Endpoint data loss prevention (Endpoint DIP) settings.
- D. The Access by unallowed apps action is set to Audit only.
- E. The unallowed browsers in the Microsoft 365 Endpoint data loss prevention (Endpoint DLP) settings are NOT configured.
Answer: C,D
NEW QUESTION 75
......
Pass Microsoft SC-400 Test Practice Test Questions Exam Dumps: https://www.prepawaypdf.com/Microsoft/SC-400-practice-exam-dumps.html
The Best Microsoft Certified: Information Protection Administrator Associate Study Guide for the SC-400 Exam: https://drive.google.com/open?id=1moDQbYXo-8Ep_CTBnzcqWtzBUT56Z4Ba