

2026 Current SPLK-1005 dumps Preparation through Our Practice Test
100% Reliable Microsoft SPLK-1005 Exam Dumps Test Pdf Exam Material
The SPLK-1005 certification exam is designed for IT professionals who are responsible for managing and maintaining Splunk Cloud environments. It covers a wide range of topics, including deployment, configuration, data management, user authentication, and troubleshooting. SPLK-1005 exam is based on a multiple-choice format, with 65 questions to be answered in 90 minutes.
Splunk is a popular platform for collecting, analyzing, and visualizing machine-generated data. As organizations increasingly rely on data to drive business decisions, the need for skilled Splunk professionals has grown. The Splunk SPLK-1005 exam is designed to certify individuals as Splunk Cloud Certified Admins. Splunk Cloud Certified Admin certification is aimed at IT professionals who are responsible for administering and managing Splunk Cloud deployments.
The SPLK-1005 exam comprises around 60 questions and has a pass mark of 75%. SPLK-1005 exam is timed and allows only 90 minutes. The test covers various aspects, including Splunk’s architecture, system installation, configuration, data management, and monitoring. SPLK-1005 exam tests the candidate’s ability to configure and deploy Splunk apps and custom alerts. Professionals who pass the certification are equipped with advanced cloud administration skills to ensure that any Splunk-based system they manage is highly available, efficient, and secure.
NEW QUESTION # 43
Which of the following are features of a managed Splunk Cloud environment?
- A. Availability of premium apps, no IP address whitelisting or blacklisting, deployed in US East AWS region.
- B. Availability of premium apps, SSO integration, IP address whitelisting and blacklisting.
- C. 20GB daily maximum data ingestion, no SSO integration, no availability of premium apps.
- D. Availability of premium apps, SSO integration, maximum concurrent search limit of 20.
Answer: B
Explanation:
In a managed Splunk Cloud environment, several features are available to ensure that the platform is secure, scalable, and meets enterprise requirements. The key features include:
Availability of premium apps: Splunk Cloud supports the installation and use of premium apps such as Splunk Enterprise Security, IT Service Intelligence, etc. SSO Integration: Single Sign-On (SSO) integration is supported, allowing organizations to leverage their existing identity providers for authentication.
IP address whitelisting and blacklisting: To enhance security, managed Splunk Cloud environments allow for IP address whitelisting and blacklisting to control access.
NEW QUESTION # 44
What is the recommended method to test the onboarding of a new data source before putting it in production?
- A. Replicate Splunk deployment in a test environment.
- B. Send data to the chance index.
- C. Send test data to a test index.
- D. Send data to the associated production index.
Answer: C
Explanation:
The recommended method to test the onboarding of a new data source before putting it into production is to send test data to a test index. This approach allows you to validate data parsing, field extractions, and indexing behavior without affecting the production environment or data.
NEW QUESTION # 45
In Splunk terminology, what is an index?
- A. A data repository that contains raw, uncompressed data along with psidx files.
- B. A data repository that contains raw, compressed data along with tsidx files.
- C. A data repository that contains raw, uncompressed data along with tsidx files.
- D. A data repository that contains raw, compressed data along with psidx files.
Answer: B
Explanation:
In Splunk, an index is a data repository that stores both raw data and associated indexing information.
Specifically, the raw data is stored in a compressed format, and the indexing information is stored in tsidx files (time series index files). These tsidx files enable fast searching and retrieval of data based on time. The correct terminology and structure make option B accurate.
Splunk Documentation Reference: Splunk Indexes
NEW QUESTION # 46
Which best practice most effectively strengthens administrative security within enterprise Splunk Cloud environments?
- A. Enforcing multi-factor authentication reduces unauthorized access risks against privileged administrative accounts significantly.
- B. Granting unrestricted administrative permissions simplifies role management and onboarding processes organization-wide efficiently.
- C. Disabling password expiration permanently improves authentication stability for distributed enterprise deployments globally.
- D. Sharing generic administrator credentials simplifies collaborative troubleshooting and auditing activities across operational teams.
Answer: A
Explanation:
Multi-factor authentication strengthens account security by requiring additional verification beyond passwords alone. This significantly reduces risks associated with compromised credentials and supports enterprise compliance requirements for protecting privileged administrative Splunk Cloud accounts.
NEW QUESTION # 47
Which of the following files is used for both search-time and index-time configuration?
- A. savesearch.conf
- B. macros.conf
- C. props.conf
- D. inputs.conf
Answer: C
NEW QUESTION # 48
Which type of forwarder is a full Splunk Enterprise instance that can run apps and add-ons?
- A. Universal forwarder
- B. Search head
- C. Deployment server
- D. Heavy forwarder
Answer: D
NEW QUESTION # 49
Which of the following methods is valid for creating index-time field extractions?
- A. Create a configuration app with the index-time props.conf and/or transfoms. conf, and upload the app via UI.
- B. Use the CU app to define settings in fields.conf, and restart Splunk Cloud.
- C. Use the rexcommand to extract the desired field, and then save as a calculated field.
- D. Use the UI to create a sourcetype, specify the field name and corresponding regular expression with capture statement.
Answer: A
Explanation:
The valid method for creating index-time field extractions is to create a configuration app that includes the necessary props.conf and/or transforms.conf configurations. This app can then be uploaded via the UI. Index- time field extractions must be defined in these configuration files to ensure that fields are extracted correctly during indexing.
Splunk Documentation Reference: Index-time field extractions
NEW QUESTION # 50
What is the name of the Splunk Cloud feature that allows you to monitor and manage resource utilization by business units and users using a Splunk app?
- A. Splunk App for Cost Optimization
- B. Splunk App for Chargeback
- C. Splunk App for Usage Analytics
- D. Splunk App for Resource Management
Answer: B
NEW QUESTION # 51
Which feature allows a light forwarder to reduce the amount of data sent to the indexer by discarding some events or fields?
- A. Data sampling
- B. Data cloning
- C. Data filtering
- D. Data masking
Answer: A
NEW QUESTION # 52
Which of the following statements is true regarding sedcmd?
- A. SEDCMD does not work on Windows-based installations of Splunk.
- B. SEDCMD can be defined in either props.conf or transforms.conf.
- C. SEDCMD uses the same syntax as Splunk's replace command.
- D. SEDCMD provides search and replace functionality using regular expressions and substitutions.
Answer: D
Explanation:
SEDCMD in props.conf applies regular expressions to modify data as it is ingested. It is useful for transforming raw event data before indexing.
NEW QUESTION # 53
How is it possible to test a script from the Splunk perspective before using it within a scripted input?
- A. splunk cmd <scriptname>
- B. splunk run <scriptname>
- C. splunk script <scriptname>
- D. ./$SPLUNK_HOME/etc/apps/<app>/bin/<scriptname>
Answer: A
Explanation:
splunk cmd <scriptname> allows running scripts in Splunk's environment for testing purposes.
This ensures the script behaves as expected within Splunk's CLI context.
NEW QUESTION # 54
What is the name of the Splunk Enterprise feature that provides a security data and event management (SIEM) solution that uses machine data to detect and respond to threats?
- A. Splunk Enterprise Intelligence
- B. Splunk Enterprise Monitoring
- C. Splunk Enterprise Analytics
- D. Splunk Enterprise Security
Answer: D
NEW QUESTION # 55
Which of the following statements is true about data transformations using SEDCMD?
- A. Configuredin props.conf and transform.conf.
- B. Can be used to manipulate the sourcetype per event.
- C. Operates on a REGEX pattern match of the source, sourcetype, or host of an event.
- D. Can only be used to mask or truncate raw data.
Answer: D
Explanation:
SEDCMD is a directive used within the props.conf file in Splunk to perform inline data transformations.
Specifically, it uses sed-like syntax to modify data as it is being processed.
* A. Can only be used to mask or truncate raw data:This is the correct answer because SEDCMD is typically used to mask sensitive data, such as obscuring personally identifiable information (PII) or truncating parts of data to ensure privacy and compliance with security policies. It is not used for more complex transformations such as changing the sourcetype per event.
* B. Configured in props.conf and transform.conf:Incorrect, SEDCMD is only configured in props.
conf.
* C. Can be used to manipulate the sourcetype per event:Incorrect, SEDCMD does not manipulate the sourcetype.
* D. Operates on a REGEX pattern match of the source, sourcetype, or host of an event:Incorrect, while SEDCMD uses regex for matching patterns in the data, it does not operate on the source, sourcetype, or host specifically.
Splunk Documentation References:
* SEDCMD Usage
* Mask Data with SEDCMD
NEW QUESTION # 56
Which type of forwarder has the lowest system resource usage and the highest data throughput?
- A. Light forwarder
- B. Heavy forwarder
- C. Universal forwarder
- D. Deployment client
Answer: C
NEW QUESTION # 57
Which of the following stanzas would enable a TCP input on port 1025, allowing traffic from all IP addresses except 10.5.5.1?
- A.
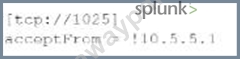
- B.
- C.
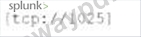
- D.
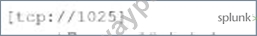
Answer: A
Explanation:
In Splunk, to configure a TCP input on a specific port and restrict traffic from certain IP addresses, you can use the acceptFrom setting. The correct stanza that enables a TCP input on port 1025 and allows traffic from all IP addresses except 10.5.5.1 would look like this:
[tcp://1025]
acceptFrom = !10.5.5.1
Here, !10.5.5.1 denotes that traffic from this IP should be denied, while all other IP addresses are allowed.
Therefore, Option B is correct.
Splunk Documentation Reference: Inputs.conf - acceptFrom
NEW QUESTION # 58
What is a private app?
- A. An app where only a specific role has read and write access.
- B. An app where only a specific role has read access.
- C. An app that is created and used only by a specific organization.
- D. An app that is only viewable by a specific user.
Answer: C
Explanation:
A private app in Splunk is one that is created and used within a specific organization, and is not publicly available in the Splunkbase app store.
An app that is created and used only by a specific organization is the correct answer. This type of app is developed internally and used by a particular organization, often tailored to meet specific internal needs. It is not shared with other organizations and remains private within that organization's Splunk environment.
NEW QUESTION # 59
Which of the following would always require raising a support ticket?
- A. A user is unable to log into Splunk Cloud.
- B. Capacity or configuration changes in Splunk Cloud.
- C. Search does not return expected results in Splunk Cloud.
- D. Data is not indexed in Splunk Cloud.
Answer: B
Explanation:
Any modifications in capacity or configurations within Splunk Cloud require an official support ticket, as they are managed by Splunk Cloud support teams to ensure consistent and secure changes.
NEW QUESTION # 60
......
Free SPLK-1005 Dumps are Available for Instant Access: https://www.prepawaypdf.com/Splunk/SPLK-1005-practice-exam-dumps.html
Based on Official Syllabus Topics of Actual Splunk SPLK-1005 Exam: https://drive.google.com/open?id=1ZnypDAmBmDOh9S8IWAV4I8feO5vBUmfA